If it is not possible to prevent a ransomware attack, how to deal with this?
Fill out the form, schedule a meeting with one of our experts and access exclusive materials to discover how Columbia and NetApp can protect your company with 30 days free Cloud Insights Premium.
Stay away from bad headlines with solutions from columbia It is NetApp.
timeline of a ransomware attack
traditional ransomware attack
without Columbia and NetApp
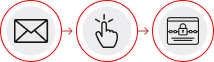
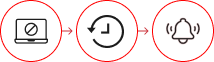
The start of the attack
The user opens the breach through an inappropriate click or malicious file and the attack begins to be operationalized, encrypting the files.
APPROACH WITH COLUMBIA AND NETAPP
Protect, Detect and Recover
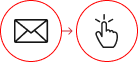
The start of the attack
The user opens the breach through an inappropriate click and the attack begins to be operationalized.
*Count on AI It is Machine Learning to detect non-standard behavior.
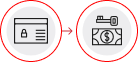
The Notification
You receive notification that your environment is compromised and are requested payment for data recovery, running the risk of negative exposure of your brand in newspaper headlines
Automatic Actions
Block suspicious user access. Ensure data integrity by automatically creating restore points and notify the administrator.
Recovery and damage minimization
The focus is to recover the environment in a race against time. But how long will it take to get operations back to normal? ?
The time will depend on how the backup is stored and the volume of data that will be restored. Another question: How to ensure that the infected file has been restored?
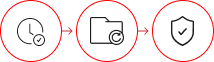
Business as usual
Fast data recovery regardless of data volume. No impact on business.
Image recovery and process/technology review
Meeting to decide how to avoid new occurrences.
Process/technology review
Continuous improvement of IT management processes.
The user opens the breach through an inappropriate click or malicious file and the attack begins to be operationalized, encrypting the files.
traditional ransomware attack
Protect, Detect and Recover
The start of the attack
The user opens the breach through an inappropriate click and the attack begins to be operationalized.
*Count on AI It is Machine Learning to detect non-standard behavior.
The Notification
You receive notification that your environment is compromised and are requested payment for data recovery, running the risk of negative exposure of your brand in newspaper headlines
Automatic Actions
Block suspicious user access. Ensure data integrity by automatically creating restore points and notify the administrator.
Recovery and damage minimization
The focus is to recover the environment in a race against time. But how long will it take to get operations back to normal? ?
The time will depend on how the backup is stored and the volume of data that will be restored. Another question: How to ensure that the infected file has been restored?
Business as usual
Fast data recovery regardless of data volume. No impact on business.
Image recovery and process/technology review
Meeting to decide how to avoid new occurrences.
Process/technology review
Continuous improvement of IT management processes.
We are a consultancy specialized in Information Security, cybersecurity and IT solutions, which always acts transparently and only works with quality products.